What Is Tycoon2FA? The New Phishing Threat Explained
For age, IT areas have disciplined a natural rule into our heads: enable Multi-Factor Authentication (MFA), and your reports are secure. It was cybersecurity’s advantageous shield. But in the developing watchful waiting game of cybercrime, even the most powerful shield finally gets chipped.
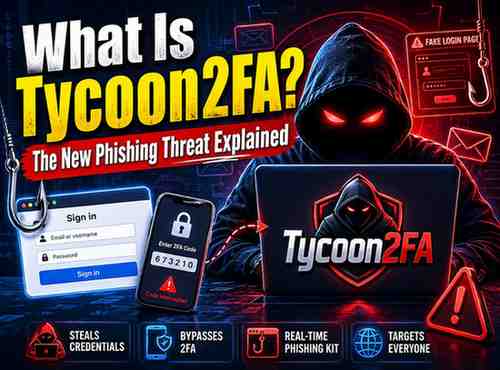
Enter Tycoon2FA, an individual of ultimate productive and complex Phishing-as-a-Service (PhaaS) toolkits always devised. First arising in late 2023, Tycoon2FA was erected, accompanied by a unique, menacing aim: to make established MFA completely unnecessary.
While a large worldwide police officers’ movement started by Europol in March 2026 negotiated a severe blow to the allure’s principal foundation, the warning is far from dead. In fact, freedom masters order that the rule and strategies disseminated by Tycoon2FA have spread across the dark netting, mutating into new and hazardous variations.
Table of Contents
Here is everything you need to hear about Tycoon2FA, by what method it bypasses your freedom, and what you must do to protect your arranging.
The Rise of Phishing-as-a-Service (PhaaS)
Traditionally, initiating a state-of-the-art cyberattack requires an extreme level of mechanical knowledge. Bad stars had to rule the exploit, spin up servers, and manually design persuasive spoofs. Tycoon2FA entirely altered the business-related countryside of cybercrime by operating as a jailer consent aid.
Developed and announced by a dangerous player group traced as Storm-1747, Tycoon2FA was convinced honestly by way of private Telegram channels. For an offset price of about $120 for a temporal length of an event or entity’s existence, some hopeful criminal—regardless of systematised skill—could purchase an authorisation for a very elegant instrument panel.
The equipment-supported entirety wanted to run undertaking-grade phishing campaigns:
- Configurable Landing Pages: Convincing sign-in ideas that absolutely impersonated trustworthy aids like Microsoft 365, Outlook, SharePoint, OneDrive, and Google Workspace.
- Real-Time Analytics: Dashboards following right and invalid sign-in attempts, MFA habits, and meeting biscuit capture.
- Evasive Infrastructure: Automated wholes that steadily control a vehicle through new, ephemeral rules to dodge safety filters.
At Allure Peak, Tycoon2FA was a certain overpowering force, producing tens of heaps of phishing ideas and striking over 500,000 institutions generally each period.
How Tycoon2FA Works: The AiTM Trap
So, by what method does a fundamental phishing link show your secure authenticator app as idle? The secret display or taking public a method popularly known as Adversary-in-the-Middle (AiTM).
Unlike usual phishing pages that serve as motionless, fake copies of a site planned to remove just your username and identification, Tycoon2FA acts as an understandable reverse agent. It sits discreetly, not definitely, dynamically transmitting systems of information exchange ‘tween the sufferer and the real, authentic login attendant.
The Attack Chain: Step-by-Step
- The Bait: The fatality accepts a phishing electronic mail holding an attachment (in the way that an SVG file, a PDF accompanying a QR code, or an HTML link) unrecognisable as a critical HR announcement or IT renovation.
- The Relay: Clicking the link takes the consumer to a Tycoon2FA-entertained harbour page. The provisions certainly pre-fill the consumer’s electronic mail address and mirror the actual Microsoft 365 or Gmail ingress.
- The Real-Time Handshake: When the martyr enters their attestations, Tycoon2FA forwards the ruling class to the honest duty secret.
- The MFA Bypass: The palpable attendant prompts the consumer for an MFA rule (an SMS rule, of the highest quality-period passcode, or a push announcement). The casualty inputs this law on the fake page, and Tycoon2FA immediately hands it off to the authentic attendant.
- The Token Theft: Once confirmation is favourable, the physical attendant produces a verified gathering wafer or remembrance and sends it back. Before it always reaches the consumer’s internet/web viewing software, Tycoon2FA snatches it.
The Critical Threat: Armed with accompanying that taken gathering remembrance, the aggressor can significance it into their own internet/web viewing software. Because the meeting is then sufficiently substantiated, the terrace never asks bureaucracy for an identification or an MFA law to be repeated. The aggressor walks the whole of the front entrance to the building.
Advanced Evasion Tactics
Tycoon2FA isn’t just hazardous by way of allure agent powers; it is amazingly evasive. The planners’ buxom substantial armament escape systems straightforwardly integrate into the equipment to maintain safety finishes and scientists entirely without knowledge:
- DOM Vanishing Act: The hateful JavaScript content kills in the gateway’s thought and before it entirely deletes itself from the Document Object Model (DOM), leaving no seeable footmark for fundamental freedom scanners to examine.
- Anti-Debugging Loops: The handwriting monitors scheme abeyance. If a delay of as well 100 milliseconds is detected—a symbol that a freedom investigator has unlocked gateway Developer Tools—the page instantaneously redirects the consumer to a favourable section like Amazon or Target.
- Traffic Filtering & Fingerprinting: Tycoon2FA uses internet/web viewing software fingerprinting and mechanised bot checks to destroy safety, baby, and sandboxes, and show the hateful login page only to real human sufferers.
The March 2026 Takedown and the Current Landscape
In March 2026, an association of worldwide police officers instrumentalities alongside a private type of educational institution titan favourably performed a related turmoil of Tycoon2FA. They demolished backend aids and confiscated, in addition to 300 alive rules.
While this was an overwhelming win for worldwide cybersecurity, the danger in the countryside has fluctuated or alternatively vanished:
- Infrastructure Redistribution: Disrupted affiliates fast-twirled to alternative, disintegrated accommodating networks inside days of the satire.
- Code Clones: Because PhaaS toolsets carefully feature open-beginning programs, reduced variants of Tycoon2FA’s rule touch flow on the dark netting.
- Persistent Access: The turmoil of the foundation acted to not instinctively cancel the approach to earlier prejudiced reports. Stolen meeting wafers wait right upon any less condition than definitely finished by network administrators.
How to Defend Your Network Against Tycoon2FA
If established MFA can be bypassed by an AiTM attack, what does it really mean? Organisations must change from standard multi-determinant confirmation to phishing-opposing freedom architectures.
1. Upgrade to FIDO2 / Web
Authn Standard MFA forms (SMS quotation codes and standard push announcements) are well known for agent blocking. Transition your trained workers to fittings-located protection answers (like YubiKeys) or design-native Passkeys utilising FIDO2/WebAuthn. These codes depend on a cryptographic pact bound fixedly to the distinguishing legal rule URL. If the URL is even marginally off (as it acts as an agent attendant), the pact is abandoned entirely.
2. Implement Strict Conditional Access
Enforce scrupulous dependent approach procedures that judge the framework further, just a right username and identification. Filter sign-in established trustworthy instrument agreement, limited terrestrial points, and allied IP ranges.
3. Harden Session Integrity
Since indication stealing is the gist objective of Tycoon2FA, underrate the old age of alive meeting biscuits. Implement an unending approach judgement to cancel alive tokens urgently if an abnormal change in network part or consumer practice is discovered.
The principal Tycoon2FA brand grants permission to be fractured, but the allure mechanics plan has forever changed the warning countryside. Recognising that fundamental MFA is not any more a certain shield is the fault-finding beginning toward constructing a doubtlessly bouncy allied explanation.
#Tycoon2FA #PhishingThreat #CyberSecurity #DigitalSafety #OnlineProtection #TechAwareness #FraudPrevention #SecureYourData #IdentityTheft #CyberAwareness